Loading Excellence
Managed Services

Cybersecurity

Threats don't stop at business hours. CloudNow monitors, manages, and responds to security risks across your Microsoft environment, helping reduce exposure before incidents become business disruptions.
Security Is Not a Projectit Requires Continuous Attention

Cyber risks

The Threat Landscape Continues to Evolve

Modern cyber threats target users, identities, devices, applications, and business processes. Understanding the risks is the first step toward building a stronger security program.

Phishing attacks

Deceptive emails, links, and messages designed to trick users into revealing information, compromising accounts, or executing malicious actions.

Ransomware

Malicious software that encrypts systems and data, disrupting operations and potentially causing significant financial and business impact.

Credential theft

Stolen usernames, passwords, tokens, or session data can provide unauthorized access to business systems and sensitive information.

Insider risks

Employees, contractors, or trusted users can intentionally or unintentionally expose data, bypass controls, or create security incidents.

Email impersonation

Attackers impersonate executives, vendors, or trusted contacts to manipulate employees, redirect payments, or obtain sensitive information.

Data Breaches

Unauthorized access, disclosure, or exfiltration of sensitive business, customer, financial, or operational data.

Challenges

Security Challenges We Help Solve

Organizations face different security risks, priorities, and resource constraints. Here are some of the most common situations where CloudNow can help.

Ransomware Risk

Configuration drift

Security settings, policies, and controls can weaken over time as systems change, users are added, and business requirements evolve.
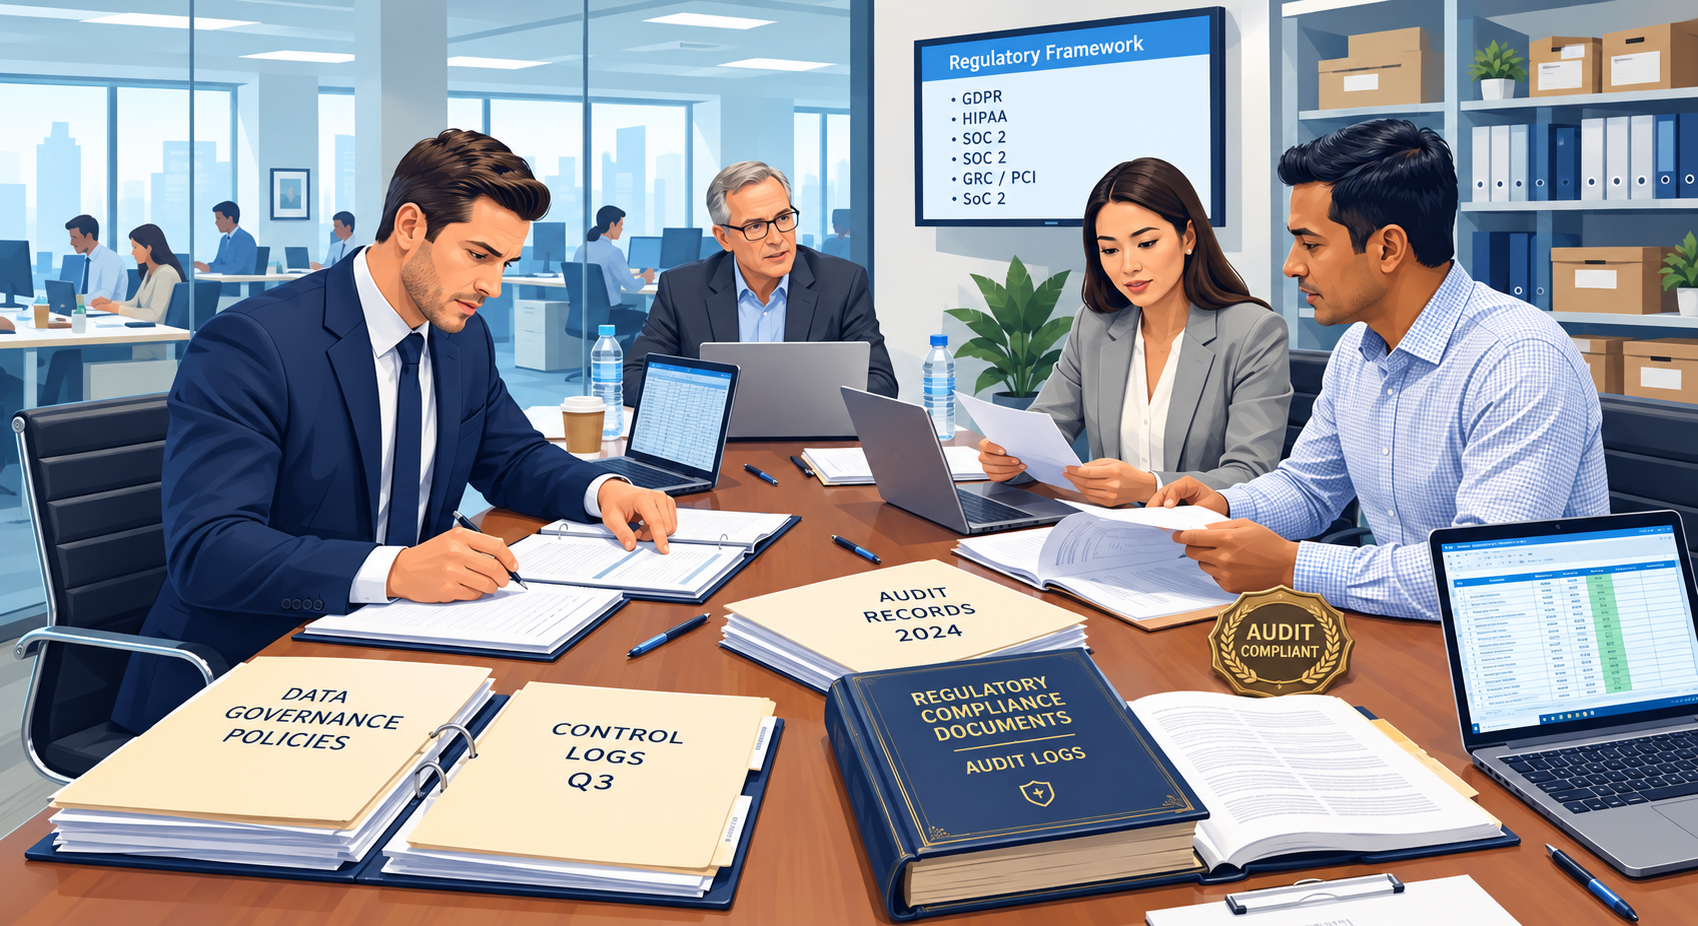
Compliance Requirements

Compliance Requirements

Help align security practices with business, regulatory, and customer compliance requirements.

Security Skill Gaps

Security Skill Gaps

Gain access to experienced security specialists without building an internal security team.

Unmanaged Alerts

Unmanaged Alerts

Turn thousands of security alerts into actionable investigations and responses.

Microsoft Defender Adoption

Microsoft Defender Adoption

Maximize the value of your existing Microsoft security investment.

Executive Visibility

Executive Visibility

Gain clearer insight into risks, trends, and overall security posture through regular reporting.

Why CloudNow

Security Isn't a Tool. It's an Ongoing Responsibility.

Deploying security software is easy. Maintaining a strong security posture requires continuous monitoring, investigation, configuration oversight, and informed decision making. CloudNow helps organizations operate security as an ongoing business function, not a one-time project.

1

Microsoft-Focused Expertise

Deep experience across Microsoft 365, Azure, Identity, Defender, and Security Operations.

2

Operational Security

Security is managed as an ongoing service, not a one-time deployment.

3

Senior-Level Guidance

Direct access to experienced cloud and security specialists.

4

Security Embedded by Design

Security is integrated across CloudNow service offerings rather than treated as a standalone add-on.

More Than Security Software

Deploying security tools is only the first step.

⠀

CloudNow MDR helps organizations move beyond simply owning security tools. Maintain an effective security posture through continuous monitoring, investigation, response, and ongoing improvement.

⠀

Security tools generate alerts. People generate outcomes.

MONITOR

Security Monitoring

We monitor security alerts, suspicious activity, and emerging risks across your Microsoft environment. Identify meaningful threats quickly while reducing alert fatigue from false positives.

Outcome: Faster identification of real threats, reduce noise from false positives alerts.

⠀

SOC 24/7 Monitoring

Continuous security monitoring outside normal business hours to help identify and respond to threats whenever they occur.

Outcome: Detect threats beyond business hours and weekends.

RESPOND

Threat Detection & Response

When security events occur, our team investigates alerts, validates potential threats, and coordinate appropriate containment and remediation actions.

Outcome: Faster incident investigation, quicker containment, and reduced business disruption.

⠀

Microsoft Defender Administration

We manage and optimize your Microsoft Defender security stack, including policies, protections, detection rules, and platform health. Ongoing review and tuning help ensure protections remain aligned with evolving threats and business requirements.

Outcome: Better protection, improved detection accuracy, and greater value from your Microsoft security investment.

IMPROVE

Vulnerability Management

Identify, assess, and prioritize security weaknesses across devices, servers, identities, and cloud resources. Focus remediation efforts on the risks that matter most rather than treating every finding equally.

Outcome: Reduced attack surface and improved security posture over time.

⠀

Security Baseline & Hardening

Review and maintain security configurations across servers, operating systems, Microsoft 365, and supporting infrastructure. Reduce unnecessary exposure by aligning systems with recommended security standards and best practices.

Outcome: More secure systems, consistent configurations, and fewer avoidable security exposures.

GOVERN

Security Configuration Oversight

Security controls can drift over time as users, devices, applications, and business requirements change. We regularly review security configurations, policies, and control settings to help maintain alignment with security objectives and recommended practices.

Outcome: Stronger security posture with consistent enforcement of recommended controls, policies, and security baselines.

⠀

Security Reporting

Regular reporting provides visibility into security events, trends, vulnerabilities, remediation activities, and overall security health. Reports are designed to support both technical stakeholders and business decision-makers.

Outcome: Visibility into security risks and executive insight. Better decision-making into cyber risk.

Platform-Based Solution

Built Around Microsoft Security Platform

⠀

Most security tools solve a specific problem. Microsoft's security platform shares intelligence across identities, endpoints, email, cloud services, and security operations to provide broader visibility and faster response.

Microsoft Defender for Endpoint

EDR

Microsoft Defender for Endpoint

Protects Windows, macOS, Linux, servers and mobile devices against ransomware, malware, and advanced threats.

Attackers frequently begin at the endpoint. Defender for Endpoint provides visibility into device activity and helps identify suspicious behavior before it spreads through the environment.

⠀

Key capabilities

✓ Endpoint detection and response (EDR)

✓ Behavioral threat analysis

✓ Automated investigation

✓ Device isolation and remediation

Protects: Devices & Servers

Microsoft Defender for Office 365

MXDR

Microsoft Defender for Office 365

Protects email, Teams, and collaboration environments from phishing, business email compromise, malicious links, and malware.

Email remains one of the most common entry points for cyberattacks. Defender helps identify and stop threats before users interact with them

⠀

Key capabilities

✓ Phishing protection

✓ Safe Links & Safe Attachments

✓ Email threat investigation

✓ Collaboration security

Protects: Email & Collaboration.

Microsoft Defender for Identity

ITDR

Microsoft Defender for Identity

Protects Active Directory and hybrid identity environments from credential theft and identity-based attacks.

Modern attackers often target user accounts rather than devices. Defender for Identity helps identify suspicious authentication activity and potential lateral movement.

⠀

Key capabilities

✓ Credential theft detection

✓ Privilege escalation monitoring

✓ Attack path analysis

✓ Identity threat detection

Protects: User Identities

Microsoft Entra ID

IAM

Microsoft Entra ID

Provides identity and access management for users, applications, and services.

Identity is the foundation of modern security. Entra ID helps ensure only authorized users access business resources under the right conditions.

⠀

Key capabilities

✓ Multi-Factor Authentication

✓ Conditional Access

✓ Single Sign-On

✓ Privileged Identity Management

Protects: Access & Authentication

Microsoft Defender XDR

XDR

Microsoft Defender XDR

Brings together signals from devices, identities, email, and cloud services into a single security investigation platform.

Rather than reviewing isolated alerts, security teams gain a unified view of incidents across the environment.

⠀

Key capabilities

✓ Cross-platform correlation

✓ Unified investigations

✓ Automated incident analysis

✓ End-to-end visibility

Protects: Entire Environment

Microsoft Sentinel

SIEM

Microsoft Sentinel

Provides centralized monitoring, analytics, automation, and reporting across the security ecosystem.

Organizations requiring enhanced visibility and compliance reporting can use Sentinel to collect and analyze security telemetry from multiple systems.

⠀

Key capabilities

✓ Security Information & Event Management

✓ Threat intelligence

✓ Security automation

✓ Centralized investigations

Protects: Security Operations

"Technology selection depends on business requirements and service scope."

Not Sure Where Your Security Risks Are?

Start the conversation with a CloudNow security specialist. Share your concerns, challenges, or goals, and we'll help you understand where to focus first.

Frequently Asked Questions

More Cybersecurity questions?

See all Cybersecurity FAQs →

Need help strengthening your security posture?

Whether you're evaluating Microsoft Defender, looking for ongoing monitoring, or reviewing your current security program, our team can help.